


[Dec 14, 2025] FCSS_NST_SE-7.6 PDF Dumps is essential on your FCSS_NST_SE-7.6 Exam Questions Certain Success!
FCSS_NST_SE-7.6 PDF Questions - Perfect Prospect To Go With FCSS_NST_SE-7.6 Practice Exam
NEW QUESTION # 38
Exhibit.
Refer to the exhibit, which shows a partial output of diagnose hardware aysinfo memory.
Which two statements about the output are true? (Choose two.)
- A. The value indicated next to the inactive heading represents the currently unused cache page.
- B. There are 98908 kB o! memory that will never be used.
- C. The I/O cache, which has 641364 kB of memory allocated to it.
- D. The user space has 708880 kB of physical memory that is not used by the system.
Answer: A,B
NEW QUESTION # 39
Exhibit.
Refer to the exhibit, which shows the output of get system ha status.
NGFW-1 and NGFW-2 have been up for a week.
Which two statements about the output are true? (Choose two.)
- A. If FGVM...649 is rebooted. FGVM...650 will become the primary and retain that role, even after FGVM...649 rejoins the cluster.
- B. If port 7 becomes disconnected on the secondary, both FortiGate devices will elect itself as primary.
- C. If no action is taken, the primary FortiGate will leave the cluster because of the current sync status.
- D. If a configuration change is made to the primary FortiGate at this time, the secondary will initiate a synchronization reset.
Answer: A,B
NEW QUESTION # 40
Refer to the exhibit, which shows partial outputs from two routing debug commands.
Which change must an administrator make on FortiGate to route web traffic from internal users to the internet, using ECMP?
- A. Set the priority of the static default route using port1 to 10.
- B. Set the priority of the static default route using port2 to 1.
- C. Set snat-route-change to enable.
- D. Set preserve-session-route to enable.
Answer: A
NEW QUESTION # 41
Refer to the exhibit, which shows the modified output of the routing kernel.
Which statement is true?
- A. The egress interface associated with static route 8.8.8.8/32 is administratively up.
- B. The default static route through 10.200.1.254 is not in the forwarding information base.
- C. The default static route through port2 is in the forwarding information base.
- D. The BGP route to 10.0.4.0/24 is not in the forwarding information base.
Answer: D
NEW QUESTION # 42
Refer to the exhibit, which a network topology and a partial routing table.
FortiGate has already been configured with a firewall policy that allows all ICMP traffic to flow from port1 to port3.
Which changes must the administrator perform to ensure the server at 10.4.0.1/24 receives the echo reply from the laptop at 10.1.0.1/24?
- A. A firewall policy that allows all ICMP traffic from port3 to port1.
- B. Enable asymmetric routing under config system settings.
- C. Change the configuration from strict RPF check mode to feasible RPF check mode.
- D. Modify the default gateway on the laptop from 10.1.0.2 to 10.2.0.2.
Answer: B
NEW QUESTION # 43
Refer to the exhibit.
The exhibit shows the output from using the command diagnose debug application samld -1 to diagnose a SAML connection.
Based on this output, what can you conclude?
- A. The authentication request is for an SSL VPN connection.
- B. The IdP IP address is 10.1.10.254.
- C. The IdP IP address is 10.1.10.2.
- D. Active Directory is used for authentication.
Answer: C
NEW QUESTION # 44
Refer to the exhibit, which contains the output of diagnose vpn tunnel list.
Which command will capture ESP traffic for the VPN named DialUp_0?
- A. diagnose sniffer packet any 'esp and host 10.200.3.2'
- B. diagnose sniffer packet any 'port 4500'
- C. diagnose sniffer packet any 'ip proto 50'
- D. diagnose sniffer packet any 'host 10.0.10.10'
Answer: B
NEW QUESTION # 45
Refer to the exhibit showing a debug output.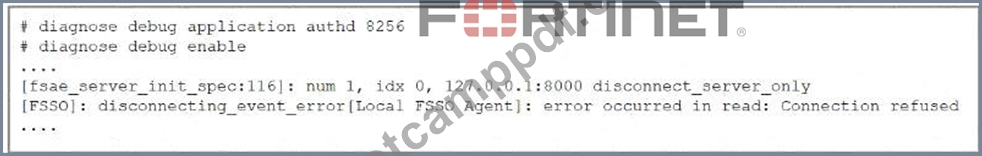
An administrator deployed FSSO in DC Agent Mode but FSSO is failing on FortiGate. Pinging FortiGate from where the collector agent is deployed is successful.
The administrator then produces the debug output shown in the exhibit.
What could be causing this error message?
- A. The TCP port 445 is blocked between FortiGate and collector agent.
- B. The FortiGate and the collector agent are using different TCP ports.
- C. The FortiGate cannot resolve the active directory server name.
- D. The collector agent preshared password is mismatched.
Answer: B
NEW QUESTION # 46
Exhibit.
Refer to the exhibit, which contains partial output from an IKE real-time debug.
Which two statements about this debug output are correct? (Choose two.)
- A. The local gateway IP address is 10.0.0.1.
- B. The initiator provided remote as its IPsec peer ID.
- C. Perfect Forward Secrecy (PFS) is enabled in the configuration.
- D. It shows a phase 2 negotiation.
Answer: B,D
NEW QUESTION # 47
Refer to the exhibit, which shows a session entry.
Which statement about this session is true?
- A. Return traffic to the initiator is sent lo 10.200.1.254.
- B. It is an ICMP session from 10.1.10.1 to 10.200.5.1.
- C. Return traffic to the initiator is sent to 10.1.0.1.
- D. It is an ICMP session from 10.1.10.10 to 10.200.1.1.
Answer: B
NEW QUESTION # 48
In the SAML negotiation process, which section does the Identity Provider (IdP) provide the SAML attributes utilized in the authentication process to the Service Provider (SP)?
- A. Authentication Request
- B. SP Login dump
- C. Assertion dump
- D. Authentication Response
Answer: C
NEW QUESTION # 49
Refer to the exhibit, which shows a partial output of the fssod daemon real-time debug command.
What two conclusions can you draw Itom the output? (Choose two.)
- A. FSSO is using agentless polling mode to detect logon events.
- B. FSSO is using DC agent mode to detect logon events.
- C. The logon event can be seen on the collector agent installed on Windows.
- D. The workstation with IP 10.124.2.90 will be polled frequently using TCP port 445 to see if the user is still logged on.
Answer: A,D
NEW QUESTION # 50
The local OSPF router is unable to establish adjacency with a peer.
Which two things should the administrator do to troubleshoot the issue? (Choose two.)
- A. Check whether both peers have an IP address within the same subnet.
- B. Check if there is an active static route to the peer.
- C. Check whether TCP port 179 is blocked.
- D. Check if IP protocol 89 is blocked.
Answer: A,D
NEW QUESTION # 51
Refer to the exhibit, which shows the output of get router info bgp summary.
Which two statements are true? (Choose two.)
- A. The TCP connection with BGP neighbor 100.64.2.254 was successful.
- B. The local FortiGate is still calculating the prefixes received from BGP neighbor 100.64.2.264
- C. The local FortiGate has received 18 packets from a BGP neighbor.
- D. The local ForliGate has received one prefix from BGP neighbor 100.64.1.254.
Answer: C,D
NEW QUESTION # 52
Exhibit.
Refer to the exhibit, which shows a FortiGate configuration.
An administrator is troubleshooting a web filter issue on FortiGate. The administrator has configured a web filter profile and applied it to a policy; however the web filter is not inspecting any traffic that is passing through the policy.
What must the administrator do to fix the issue?
- A. Disable webfilter-force-off.
- B. Increase webfilter-timeout.
- C. Enable fortiguard-anycast.
- D. Change protocol to TCP.
Answer: A
NEW QUESTION # 53
Which two statements about an auxiliary session ate true? (Choose two.)
- A. With the auxiliary session selling disabled, only auxiliary sessions are offloaded.
- B. With the auxiliary session setting enabled. Iwo sessions are created in case of routing change.
- C. With the auxiliary session setting enabled. ECMP traffic is accelerated to the NP6 processor.
- D. With the auxiliary session setting disabled, for each traffic path. FortiGate uses the same auxiliary session.
Answer: B,C
NEW QUESTION # 54
Refer to the exhibit, which shows the output of get router info ospf neighbor.
What can you conclude from the command output?
- A. All neighbors are in area 0.0.0.0.
- B. The local FortiGate is not a DROther.
- C. The network type connecting the local Fortigate and OSPF neighbor 0.0.0.10 is point-to-point.
- D. The local FortiGate is the BDR.
Answer: C
NEW QUESTION # 55
In IKEv2, which exchange establishes the first CHILD_SA?
- A. IKE_SA_INIT
- B. CREATE_CHILD_SA
- C. IKE_Auth
- D. INFORMATIONAL
Answer: B
NEW QUESTION # 56
Which two statements are true regarding heartbeat messages sent from an FSSO collector agent to FortiGate?
(Choose two.)
- A. The heartbeat messages must be manually enabled on FortiGate.
- B. The heartbeat messages can be seen in the collector agent logs.
- C. The heartbeat messages can be seen on FortiGate using the real-lime FSSO debug.
- D. The heartbeat messages can be seen using the command diagnose debug authd fsso list.
Answer: B,C
NEW QUESTION # 57
Consider the scenario where the server name indication (SNI) does not match either the common name (CN) or any of the subject alternative names (SAN) in the server certificate.
Which action will FortiGate take when using the default settings for SSL certificate inspection?
- A. FortiGate uses the CN information from the Subject field in the server certificate.
- B. FortiGate uses the SNI from the user's web browser.
- C. FortiGate uses the first entry listed in the SAN field in the server certificate.
- D. FortiGate closes the connection because this represents an invalid SSL/TLS configuration.
Answer: A
NEW QUESTION # 58
Exhibit.
Refer to the exhibit, which shows the output of diagnose automation test.
What can you observe from the output? (Choose two.)
- A. An HA failover occurred.
- B. The test was unsuccessful.
- C. The automation stitch test is not being logged.
- D. The automation stitch test failed but the HA failover was successful.
Answer: B,C
NEW QUESTION # 59
Refer to the exhibits, which contain the partial configurations of two VPNs on FortiGate.
An administrator has configured two VPNs for two different user groups. Users who are in the Users-2 group are not able to connect to the VPN. After running a diagnostics command, the administrator discovers that FortiGate is not matching the user-2 VPN for members of the Users-2 group.
Which two changes must the administrator make to fix the issue? (Choose two.)
- A. Enable XAuth on both VPNs.
- B. Use different pre-shared keys on both VPNs.
- C. Change to aggressive mode on both VPNs.
- D. Set up specific peer IDs on both VPNs.
Answer: C,D
NEW QUESTION # 60
Refer to the exhibits.
An administrator is attempting to advertise the network configured on port3. However, FGT-A is not receiving the prefix.
Which two actions can the administrator take to fix this problem? (Choose two.)
- A. Restart BGP using a soft reset to force both peers to exchange their complete BGP routing tables.
- B. Use the set network-import-check disable command.
- C. Modify the prefix using the network command from 172.16.0.0/16 to 172.16.54.0/24.
- D. Manually add the BGP route on FGT-A.
Answer: B,C
NEW QUESTION # 61
Refer to the exhibit, which shows the partial output of a real-time OSPF debug.
Why are the two FortiGate devices unable to form an adjacency?
- A. The Hello packet is being sent from an OSPF router with ID 0.0.0.112.
- B. The passwords on the FortiGate devices do not match.
- C. The two FortiGate devices attempting adjacency are in area 0.0.0.0.
- D. One FortiGate device is configured to require authentication, while the other is not.
Answer: D
NEW QUESTION # 62
Exhibit.
Refer to the exhibit, which contains a screenshot of some phase 1 settings.
The VPN is not up. To diagnose the issue, the administrator enters the following CLI commands on an SSH session on FortiGate:
However, the IKE real-time debug does not show any output. Why?
- A. The administrator must also run the command diagnose debug enable.
- B. The log-filter setting is incorrect. The VPN traffic does not match this filter.
- C. The debug shows only error messages. If there is no output, then the phase 1 and phase 2 configurations match.
- D. Replace diagnose debug application ike -1 with diagnose debug application ipsec -1.
Answer: A
NEW QUESTION # 63
......
FCSS_NST_SE-7.6 Exam with Accurate FCSS - Network Security 7.6 Support Engineer PDF Questions: https://examcollection.bootcamppdf.com/FCSS_NST_SE-7.6-exam-actual-tests.html